Security
Built like it holds the keys. It does.
Orchec drives the servers your business runs on, so it is built to the standard that deserves: an outbound-only agent, one authorization path for every action, envelope-encrypted secrets, and an audit log of everything people, bots and AI do.
Outbound-only agent
One encrypted connection out over port 443. No inbound port, and no SSH keys held by Orchec.
Roles and two-factor
Owner, admin, developer and viewer, scoped to an organization, project, server or site. TOTP and passkeys.
Secrets stay secret
Envelope-encrypted per organization, masked by default, and every reveal is logged with who and when.
Everything on the record
Every action with who, what, when, IP and result, exportable, including every prompt and plan from the AI.
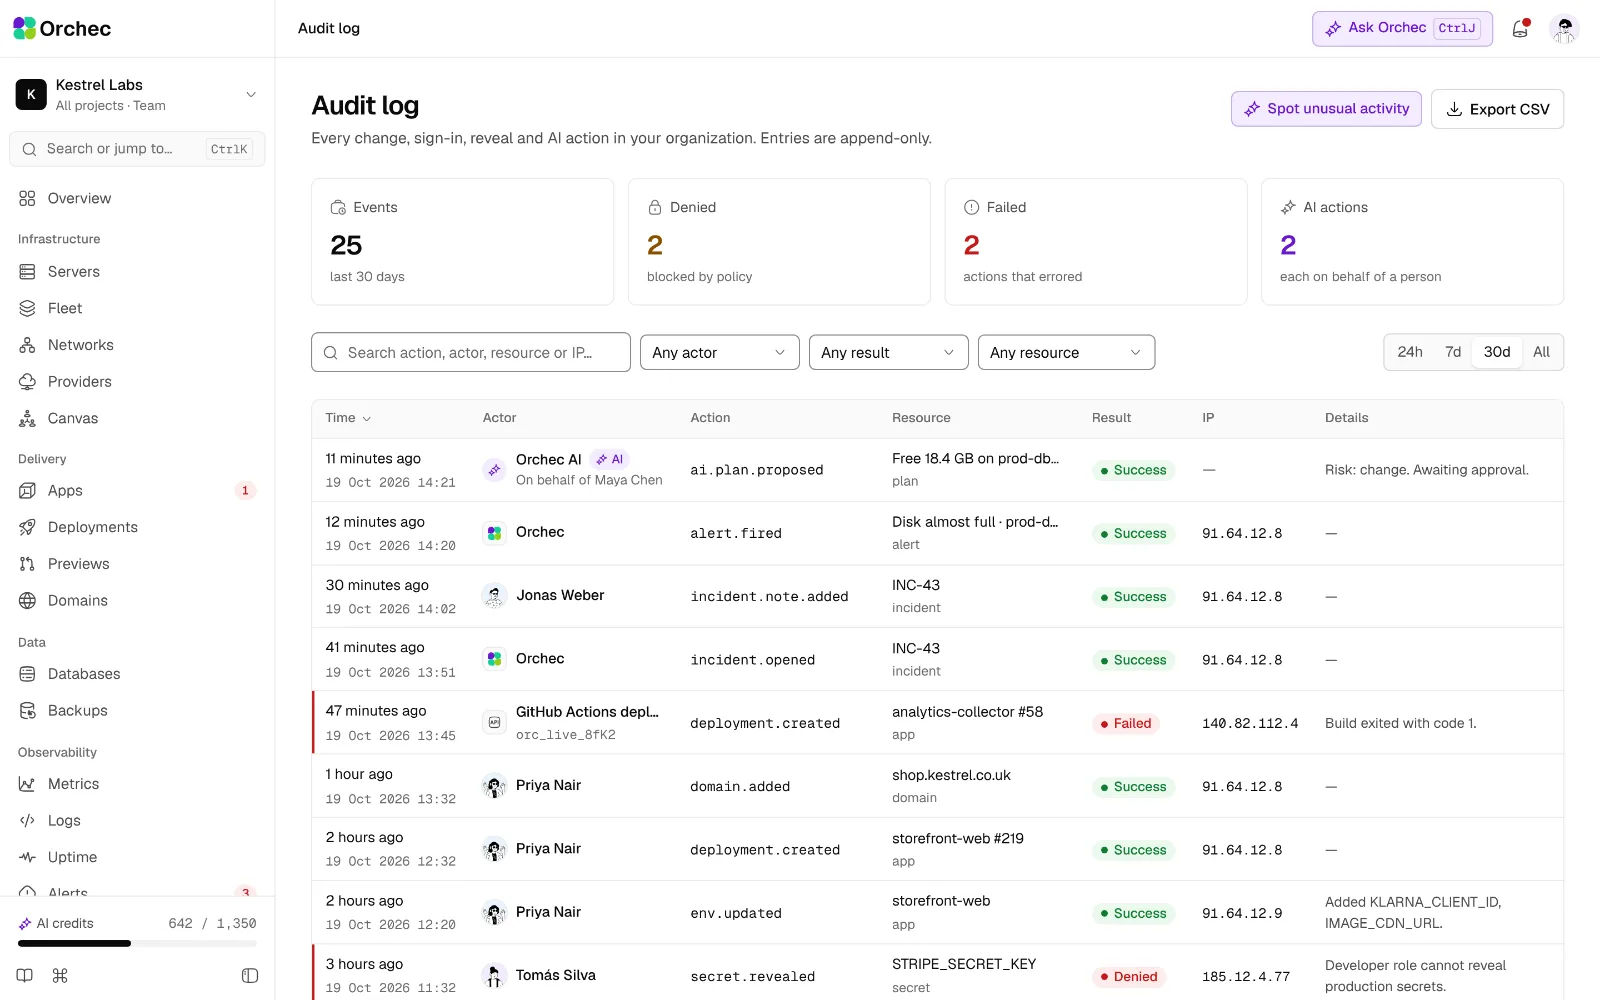
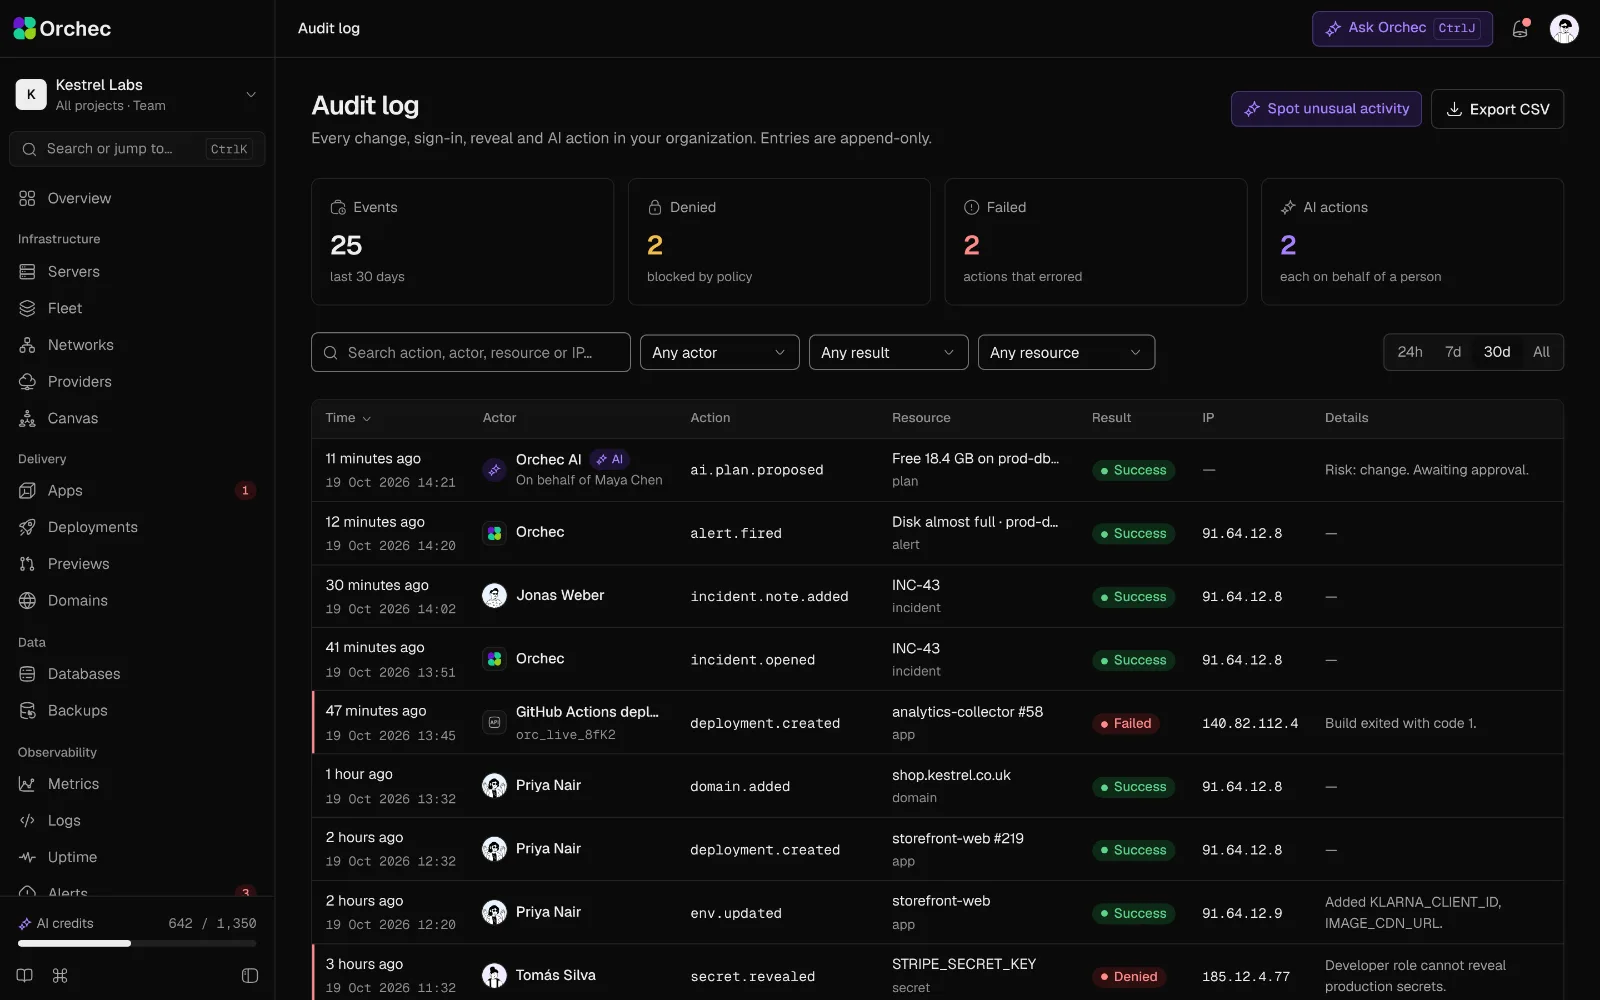
The audit log: who did what, when, from where, and with what result.
Access and identity
Who can do what, and where.
Secure server defaults
Root login off, key-only SSH, firewall on, fail2ban and automatic security updates.
Access and identity
SSH key management
Add and remove keys per server and per person.
Access and identity
Two-factor and passkeys
TOTP and WebAuthn passkeys.
Access and identity
Roles and scopes
Owner, admin, developer and viewer, scoped to org, project, server or site.
Access and identity
Site isolation
Each site runs under its own Linux user.
Access and identity
Session management
See active sessions and end them.
Access and identity
Organizations and projects
Group servers and apps by client or product.
Teams and organizations
Invitations
Invite by email with a chosen role.
Teams and organizations
Ownership transfer
Move servers and projects between people or organizations.
Teams and organizations
Activity feed
Recent actions across the organization.
Teams and organizations
On the roadmap · 6 more
- Single sign-onGoogle, GitHub, Microsoft and any OIDC or SAML provider.
- Custom rolesPick permissions one by one.
- Panel IP allow listRestrict dashboard access by IP.
- AI access review AIA monthly review that flags unused admins, stale keys and over-broad roles, with one-click fixes.
- White-labelAgencies brand the panel for their clients.
- Agency mode and client portalClients get a read-only view of their sites, uptime and backups.
Secrets
Encrypted, masked and audited.
Secrets vault
Envelope-encrypted secrets per organization.
Masked by default
Revealing a secret is logged with who and when.
On the roadmap · 5 more
- Secret referencesUse ${secret.DB_URL} in env files instead of pasting values.
- Leak detectionFinds secrets in logs and repositories.
- Rotation workflowsRotate a database password and redeploy every app that uses it.
- External secret managersHashiCorp Vault, AWS Secrets Manager, Doppler and 1Password.
- AI secret scanner AIFinds keys committed to repos, logs or env files and walks you through rotating them.
Hardening and vulnerabilities
Secure defaults, and warnings when something drifts.
Open-port watch
Alerts when a database or admin port becomes public.
Login and SSH activity
Failed logins, new SSH sessions and sudo use.
On the roadmap · 6 more
- Vulnerability reportOutdated packages and known CVEs per server.
- Hardening scoreCIS-style checklist score per server with one-click fixes.
- Image and dependency scanContainer images and lockfiles checked for known CVEs.
- Malware and rootkit scanClamAV and rkhunter on a schedule.
- AI security advisor AIRanks findings by real exposure and explains each fix in plain words.
- AI attack-pattern detection AIFlags brute force, port scans and unusual logins from auth and proxy logs.
Audit and compliance
A trail you can hand to an auditor.
Audit log
Every action with who, what, when, IP and result; exportable.
On the roadmap · 4 more
- Approval policiesDestructive actions need a second approver.
- Configuration historySee any server's config, packages and services as they were on a past date.
- Compliance evidence exportEvidence packs for SOC 2 and ISO 27001 controls.
- AI audit search AI"Who changed the firewall on prod-db last week?" answered from the audit log.
Be first in when Orchec opens.
Join the waitlist for an early invite, or book a demo and we’ll walk your team through it on your own stack.